Let’s be direct about something most cybersecurity professionals already feel but rarely say out loud: the payment security landscape didn’t just change when PCI DSS v4.0 arrived. It fractured. The old assumption that compliance equaled security — always a dangerous oversimplification — finally collapsed under the weight of increasingly sophisticated attacks, cross-border regulatory complexity, and the sheer speed of digital payment adoption across markets that were barely on the radar five years ago.
India’s UPI ecosystem processed over 100 billion transactions in 2024 alone. The MENA digital payments market is on a trajectory toward USD 422.56 billion by 2030. South Africa’s mobile money sector is expanding faster than its regulatory frameworks can comfortably accommodate. Across these markets, one thing is consistent: the attack surface is growing faster than most organizations’ capacity to defend it.
So when 4,000+ senior cybersecurity, IT, and GRC professionals gather across six countries in 2026 to specifically address payment security — not as a side topic at a general fintech conference, but as the entire point — that’s not a conference circuit. That’s a response to a genuine crisis of readiness.
This is the moment payment security professionals can’t afford to sit out.
The PCI DSS v4.0 Reality Check
The deadline passed. April 1, 2025 marked the full enforcement of PCI DSS v4.0, ending the transition period from v3.2.1 that many organizations treated, in practice, as extended breathing room. Some used that time well. Many didn’t.
PCI DSS v4.0 isn’t just a version update in the way software patches work — where the core architecture stays the same and you’re applying fixes. v4.0 represents a genuine philosophical shift in how the standard approaches security. The move toward customized implementation, where organizations can achieve compliance objectives through approaches tailored to their specific environment rather than following prescriptive requirements to the letter, demands a different kind of security leadership. It demands people who understand the intent behind controls, not just their mechanical application.
That’s harder. It requires deeper expertise, better documentation, more sophisticated risk assessment, and a closer relationship between security teams and auditors. Organizations that built their compliance programs around checkbox culture are finding v4.0 genuinely uncomfortable — and that discomfort is, frankly, the point.
For organizations that have been coasting on legacy compliance programs, 2026 is the year the coasting stops. Assessors are applying the standard as written, not as it was informally interpreted during the transition period.
Why the Middle East Is at the Center of This Conversation
The UAE’s decision to mandate PCI DSS alignment across its financial services sector wasn’t just regulatory housekeeping. It was a signal — one that the rest of the region read correctly. When a market as internationally interconnected as Dubai’s financial hub sets a hard line on cardholder data security standards, it sends pressure through every institution that touches that market. Correspondent banks, payment processors, e-commerce platforms serving UAE customers from other GCC countries, logistics companies that handle in-transit payments — all of them suddenly have a compliance question that wasn’t as urgent before.
The UAE fintech sector’s rapid growth compounds this. New entrants arrive constantly, many of them building payment flows before they’ve fully internalized what securing those flows actually requires. The speed of market entry has, in some cases, outpaced security maturity in ways that will become visible as attack sophistication increases.
Saudi Arabia’s situation is different but equally urgent. Vision 2030’s financial services transformation goals have driven aggressive digital payment adoption — which is exactly what they were designed to do. But rapid adoption creates rapid exposure. The Saudi Payment Security Summit’s success in 2024 pointed to genuine hunger among KSA security professionals for substantive, peer-level conversations about how to navigate that exposure. Not vendor pitches. Actual knowledge exchange between practitioners who are dealing with the same problems under the same regulatory framework.
Oman follows a pattern seen across the GCC: a relatively smaller market with strong regulatory intent, where the compliance challenge is often less about willingness and more about capacity. Finding qualified PCI QSAs, building internal expertise, and accessing peer networks that help interpret ambiguous requirements — these are practical problems, and they don’t get solved by reading the standard in isolation.
India’s Payment Security Challenge Is Unlike Any Other

The scale of India’s digital payment ecosystem creates a security challenge that has no real parallel elsewhere in the world. When UPI transactions grow 44% year-on-year, and when platforms like PhonePe and Google Pay collectively handle a substantial portion of the country’s retail transactions, the security implications ripple outward in ways that even sophisticated security teams struggle to fully map.
The Reserve Bank of India’s enforcement of stringent payment security guidelines — aligned with PCI DSS — has created a compliance baseline, but baseline compliance in a market of this velocity is a moving floor. Merchants and payment processors that were comfortably compliant eighteen months ago may find their control environments straining under transaction volumes and integration complexity they didn’t anticipate.
There’s also the ecosystem diversity problem. India’s payment stack involves banks, payment aggregators, payment gateways, merchants, and a regulatory layer that is actively evolving. Each of these participants has a slightly different relationship with the cardholder data environment. Each has different security maturity levels, different technical infrastructures, and different interpretations of where their compliance obligations begin and end. The interaction points between these participants are where the real risk concentrates.
Security professionals in India working on payment systems aren’t dealing with a simple problem with a known solution. They’re navigating a genuinely complex, fast-moving environment where the right answer in one segment of the ecosystem may create problems in another. The most valuable thing those professionals can do — besides staying current on the technical requirements — is talk to each other. Rigorously. Honestly. With the specific context of their market, not in the abstract.
The Sectors That Are Most Exposed — And Least Prepared
Not all industries within the payment security conversation are equally positioned. Some sectors have been navigating PCI DSS compliance for long enough that the processes, while demanding, are familiar. Others are coming to serious compliance for the first time, driven by the expansion of digital payment channels into their operations.
Retail and E-Commerce has been on the front line of payment security for years, but the attack surface keeps expanding. The shift toward omnichannel retail — where a customer might initiate a transaction on a mobile app, complete it through a website, and pick up goods in a physical store — creates integration complexity that is genuinely hard to secure. Each touchpoint is a potential exposure. Web skimming (Magecart-style attacks) has hit large retailers hard; the requirement under PCI DSS v4.0 for script integrity controls on payment pages is a direct response, and many e-commerce operations are still working through what implementation actually requires in their specific technical environment.
Insurance is going through a payment security reckoning that many in the sector didn’t fully anticipate. As insurers have digitized premium collection, claims disbursement, and policyholder management, they’ve become de facto payment processors in ways their compliance programs weren’t originally built to handle. The cardholder data environment in a modern insurance operation can be surprisingly large and difficult to scope accurately.
Travel and Tourism presents one of the most complex PCI DSS scoping challenges in any industry. Booking platforms, OTAs, airlines, hotels, car rental companies, and tour operators all touch payment data at different points in a customer’s journey. The tokenization and encryption requirements that straightforward retail operations apply relatively cleanly become genuinely complicated when payment data flows across multiple systems operated by different organizations in different jurisdictions.
What GRC Professionals Are Getting Wrong About Payment Security
Governance, Risk, and Compliance professionals occupy a specific and sometimes frustrating position in the payment security conversation. Their role is to ensure that compliance programs are functioning, that risks are being documented and managed, and that the organization can demonstrate its security posture to assessors, regulators, and leadership. That’s genuinely important work.
But GRC frameworks applied to payment security can create a dangerous illusion of coverage when the underlying security controls are weaker than the documentation suggests. This isn’t a criticism of GRC professionals — it’s a structural problem. When compliance is the primary metric, the incentive is to achieve compliance rather than to achieve security. These aren’t always the same thing, and in payment security, the gap between them can be expensive.
PCI DSS v4.0’s push toward risk-based approaches and customized implementations is partly designed to close this gap. When organizations have to articulate why a control is appropriate for their specific environment, rather than simply showing that a prescriptive requirement has been met, it becomes harder to paper over underlying weaknesses. Assessors are asking harder questions. Evidence requirements are more demanding. The documentation of the thinking behind compliance decisions matters as much as the decisions themselves.
The Online Visibility Problem Nobody Talks About
Here’s something that sits adjacent to the technical security conversation but affects it in practical ways: many of the organizations most in need of quality payment security information and resources can’t find the right content because the digital presence of specialist providers in this space is poorly optimized.
A CISO at a mid-size retailer in Riyadh researching PCI DSS v4.0 implementation approaches, or a GRC manager in Bangalore looking for guidance on cardholder data scoping in a UPI-heavy transaction environment, shouldn’t have to work hard to find the information that exists. But search results in specialized domains like payment security are notoriously noisy — dominated by generic content, outdated documentation, and vendor material with obvious commercial intent rather than genuine educational value.
Organizations and platforms that produce substantive payment security content face a discoverability problem that isn’t solved by content quality alone. Technical SEO, structured site architecture, and search engine understanding of what a site covers and who it serves — these are the infrastructure that lets good content actually reach the people looking for it. It’s the same challenge any specialist knowledge provider faces: expertise is only valuable if the people who need it can locate it. Agencies that work specifically in the B2B professional services and events space,understand that the SEO requirements for a conference series or a specialist knowledge platform are fundamentally different from standard e-commerce or consumer content optimization.
This matters in the payment security context because the quality of information available to practitioners shapes the quality of their security programs. When a GRC professional in a sector new to serious compliance can find accurate, current, practitioner-level guidance through a search rather than having to rely entirely on their vendor relationships, the whole ecosystem gets stronger.
The Multi-Country Summit Format: Why It Works
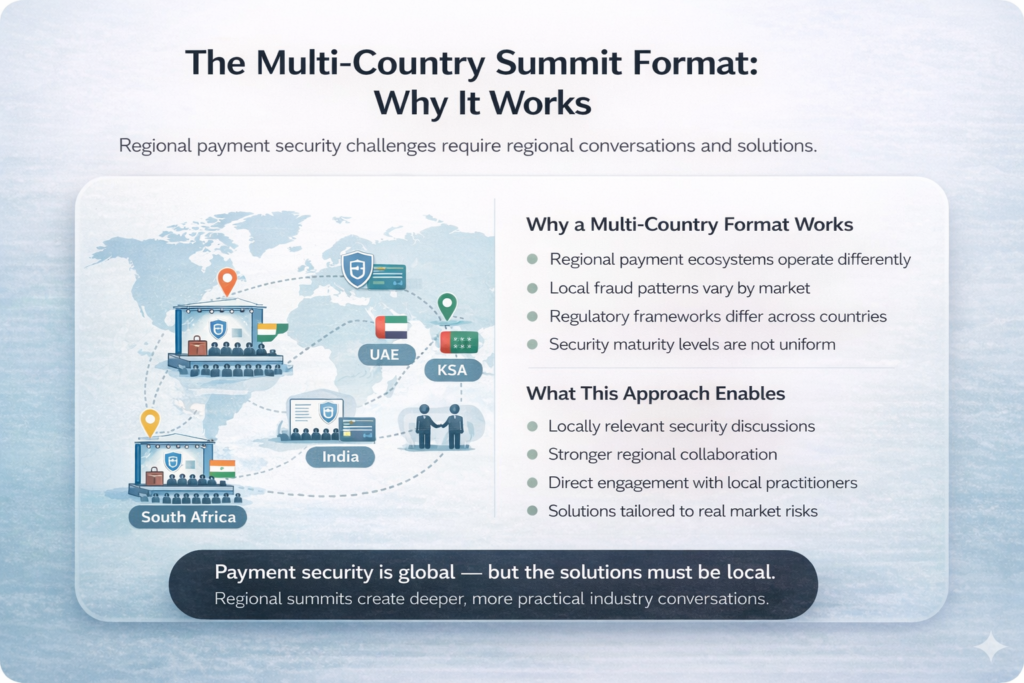
There’s a temptation, when planning professional events, to consolidate. One big event, one central location, maximum economies of scale. The logic is financially appealing and logistically clean.
It’s also wrong for the payment security context — and the Payment Security Summit Series 2026’s six-country format reflects a genuine understanding of why.
Payment security is not a uniform problem. The threat landscape in South Africa is different from the threat landscape in India, which is different from the UAE, which is different from KSA. The regulatory frameworks differ. The dominant payment mechanisms differ. The maturity levels of institutional security programs differ. The composition of the practitioner community differs. A CISO from an Omani bank has different immediate concerns than a security architect from an Indian payment aggregator — even though they’re both working within PCI DSS frameworks.
When you put those practitioners in the same room, the conversation that happens is valuable but necessarily general. When you run country-specific editions, you can get specific. You can build an agenda around the actual compliance challenges facing institutions in that regulatory environment. You can bring in speakers who have firsthand experience with the specific assessors, regulators, and threat actors active in that market. You can create space for the candid conversations that happen when everyone in the room is navigating the same specific context.
What Needs to Happen in the Room in 2026
If you spend time with payment security professionals — not in their official capacity, not in the prepared remarks they give to regulators, but in genuine conversation — certain themes emerge consistently.
The scoping conversation needs to get harder. PCI DSS assessments live or die on scope, and scope is where most compliance programs are weakest. Organizations systematically underestimate their cardholder data environment, not always from bad faith but because modern digital payment flows are genuinely complex and the data surfaces up in unexpected places. The conversation about how to scope accurately in omnichannel, multi-processor, cloud-native payment environments isn’t being had rigorously enough.
Third-party risk in the payment chain is understated. When a retailer uses a payment gateway that uses a processor that uses a sponsor bank, the security of the retailer’s cardholder data depends on the security programs of entities three steps removed. The contractual frameworks that govern these relationships — and the practical oversight that’s actually exercised — are often weaker than the organizational chart suggests they should be.
Incident response for payment breaches requires different muscles than general incident response. The forensics, notification requirements, remediation obligations, and reputational management of a payment breach have specific characteristics that general IR programs frequently don’t address. Organizations that find this out during an actual incident rather than in preparation are in a significantly worse position.
The human factor doesn’t get enough attention. Social engineering attacks targeting payment authorization personnel — specifically designed to exploit the pressure to process transactions quickly — are becoming more frequent and more sophisticated. Technical controls matter enormously, but the security of payment authorization ultimately rests on trained human judgment under pressure. Training programs for payment-facing staff haven’t kept pace with the sophistication of current attacks.
These are the conversations that need to happen in 2026. Not in generalities, not in vendor pitches, but in specific, experienced, peer-to-peer exchange. That’s what a well-constructed summit actually provides when it’s built around practitioners rather than around sponsors.
What Senior Professionals Should Be Doing Right Now
The window between now and the 2026 summit series is not a passive waiting period. For cybersecurity, IT, and GRC professionals who take payment security seriously, it’s a preparation window.
Map your current compliance posture honestly. Not how your documentation describes it — how it actually is. Where are the gaps between what your control framework says and what your technical environment actually does? Identifying those gaps before an assessment does is the difference between a finding you’ve already remediated and a finding that drives a remediation timeline.
Review your scope documentation against your actual transaction flows. Payment data flows change. New integrations, new channels, new partners. Scope documentation that was accurate eighteen months ago may not reflect current reality. A manual review against actual data flows is not optional — it’s the foundation of a credible compliance program.
Build or strengthen your peer network. The professionals who handle payment security incidents most effectively aren’t necessarily the ones with the most internal resources — they’re the ones who know who to call. Investing in professional relationships before a crisis means those relationships exist when you need them.
Look seriously at the customized approach. If your organization has security controls that go beyond PCI DSS prescriptive requirements in some areas, the customized implementation path under v4.0 may actually reduce your compliance burden while strengthening your actual security posture. This requires a sophisticated conversation with your QSA, but it’s a conversation worth initiating.
Plan your 2026 professional development calendar around the events that will actually move your program forward. The payment security summit series hitting six countries means that wherever you’re based in MENA, APAC, or Africa, there’s likely an edition close enough to justify attendance. The ROI of those events isn’t in the sessions — it’s in the conversations that happen around them.
The Bigger Picture
Payment security is often framed as a compliance problem. That framing is understandable — compliance deadlines, assessor relationships, and regulatory consequences are immediate and concrete in a way that the diffuse risk of “being breached someday” isn’t.
But payment security is actually a trust problem. The entire architecture of digital commerce rests on the assumption that payment data can be transmitted, stored, and processed without being stolen, manipulated, or exposed. When that assumption fails — at scale, publicly, in markets where digital payment adoption is still in its growth phase — the damage isn’t just financial. It’s behavioral. People stop using digital payment channels. They revert to cash. The infrastructure that took years of investment to build loses adoption in months.
The senior professionals who attend payment security summits in 2026 aren’t just protecting their organizations from fines and findings. They’re protecting the trust that makes digital commerce possible in their markets. That’s a different kind of motivation, and it tends to produce a different quality of conversation.
The work is technical. The compliance requirements are detailed and demanding. But underneath all of it, this is a conversation about whether the infrastructure of modern economic life is built on foundations that can be trusted. That’s the conversation worth having — and 2026 is the year to have it.